Vendor Evaluation3 September 2026
AI Vendor Independence: How to Prove You Are Not Locked In
Lock-in is not a feeling, it is a measurable exit cost. The seven layers where AI vendors trap buyers, and the evidence that proves independence.
EU AI regulation, operationally
Operational guidance on the AI Act, NIS2, GDPR/DORA and the Cyber Resilience Act for teams that have to put AI through a supplier audit. Every regulatory date we publish is checked against EUR-Lex or a Commission source, with the access date recorded.
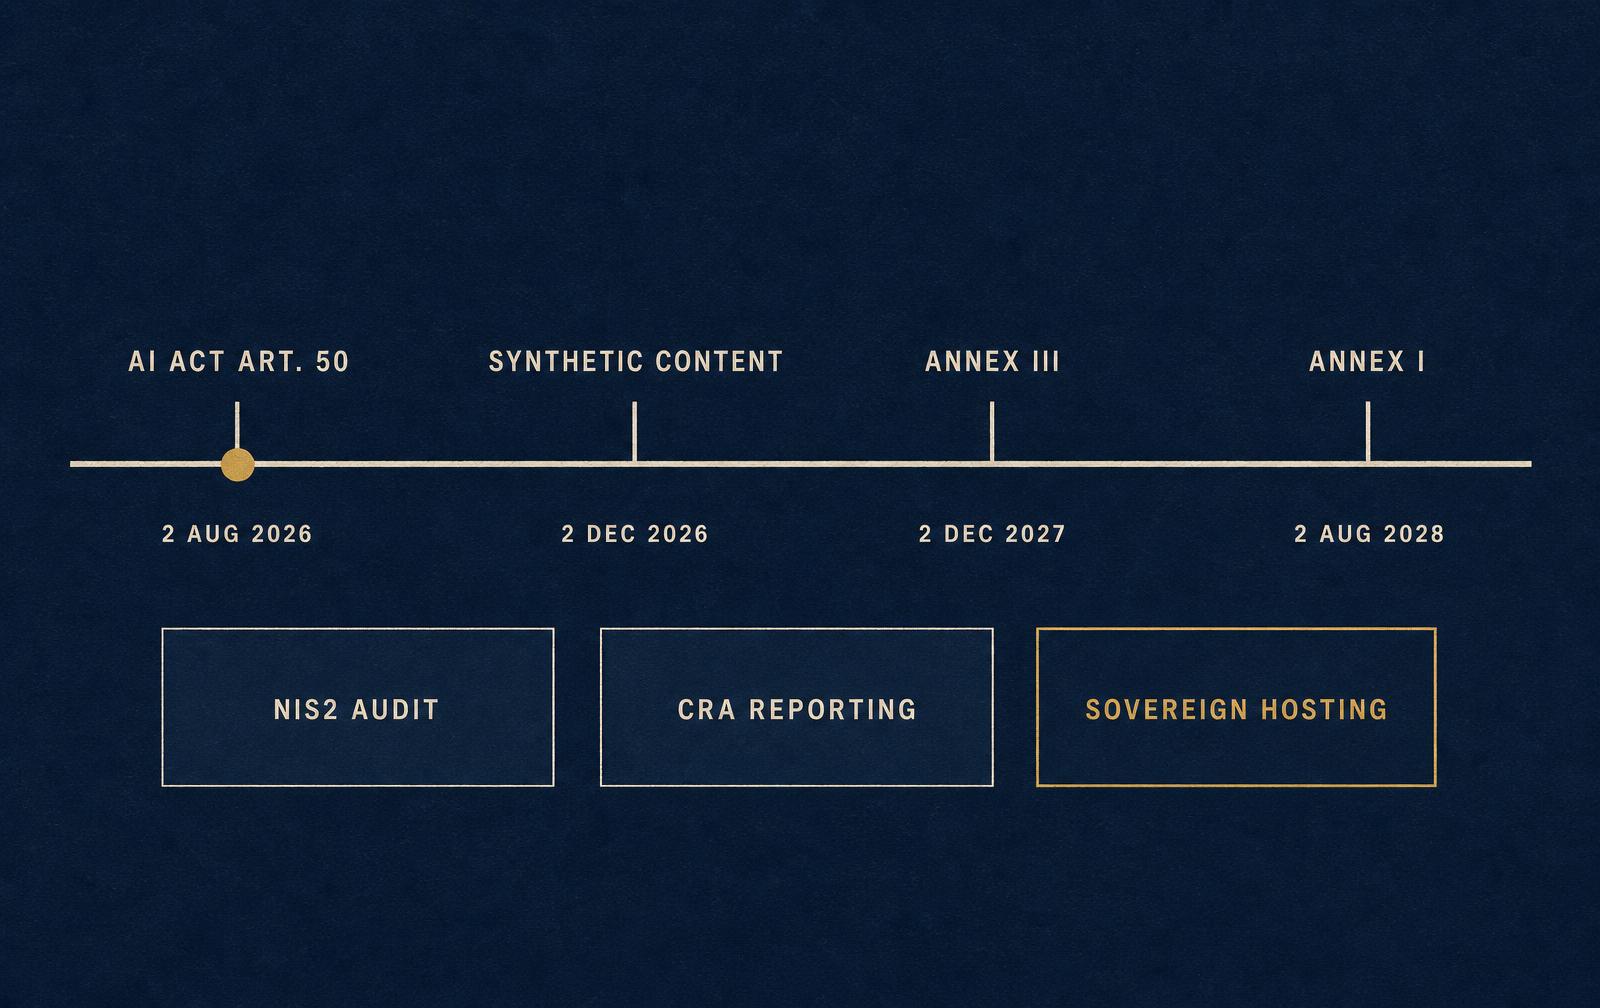
The Digital Omnibus of 27 July 2026 deferred the AI Act high-risk regime. Most published roadmaps still use the old calendar.
2 Aug 2026
AI Act Article 50 applies
11 Sep 2026
CRA Article 14 incident reporting
12 Sep 2026
Data Act: data by design
2 Dec 2026
Marking grace period ends
12 Jan 2027
Switching egress fees end
2 Dec 2027
Annex III high-risk obligations
Featured
Lock-in is not a feeling, it is a measurable exit cost. The seven layers where AI vendors trap buyers, and the evidence that proves independence.
The 31 questions a NIS2 supply chain audit puts to an AI vendor, grouped by theme, each with the artefact that closes it and the answers that fail.
A line-by-line three-year cost comparison of metered API inference, European managed hosting and owned on-premise AI capacity, with the break-even points.
Content clusters
The flagship cluster: AI Act, NIS2, GDPR/DORA and the Cyber Resilience Act treated as one obligation map, with confirmed dates and primary sources.
What buyers actually mean by sovereign AI, and the architecture decisions behind it: jurisdiction, isolation, retrieval and hardware.
Hand-written comparisons and buying tools: TCO, deployment models, exit clauses and the questions that expose compliance debt in an RFP.
One template applied per sector: risk, use case, proof, rollout. Sectors are added on signals from search and citations, not planned in advance.
Where the reading leads
Map your AI system against Article 50 transparency duties and the deferred high-risk obligations, with dates verified in EUR-Lex.
DetailsSupply-chain security evidence for AI vendors audited by essential and important entities under NIS2, including CRA incident timelines.
DetailsChoose between on-prem, air-gapped, network-isolated and private-cloud AI with the numbers and the audit consequences of each option.
DetailsNIS2 has 46 articles. Only a handful reach an AI vendor. A plain-language map of which ones bind you directly, which reach you through your customer, and what each demands.
From 11 September 2026, Article 14 of the Cyber Resilience Act obliges manufacturers to report actively exploited vulnerabilities and severe incidents. The three deadlines, who files where, and what an AI vendor needs ready.
Lock-in is not a feeling, it is a measurable exit cost. The seven layers where AI vendors trap buyers, and the evidence that proves independence.
Next step
Send the customer questionnaire, RFP section or audit request that is blocking a deal. We reply with the gaps we see and what closing them takes.
Request a review