Directive (EU) 2022/2555: Which Articles Bind an AI Vendor
NIS2 has 46 articles. Only a handful reach an AI vendor. A plain-language map of which ones bind you directly, which reach you through your customer, and what each demands.
Cluster
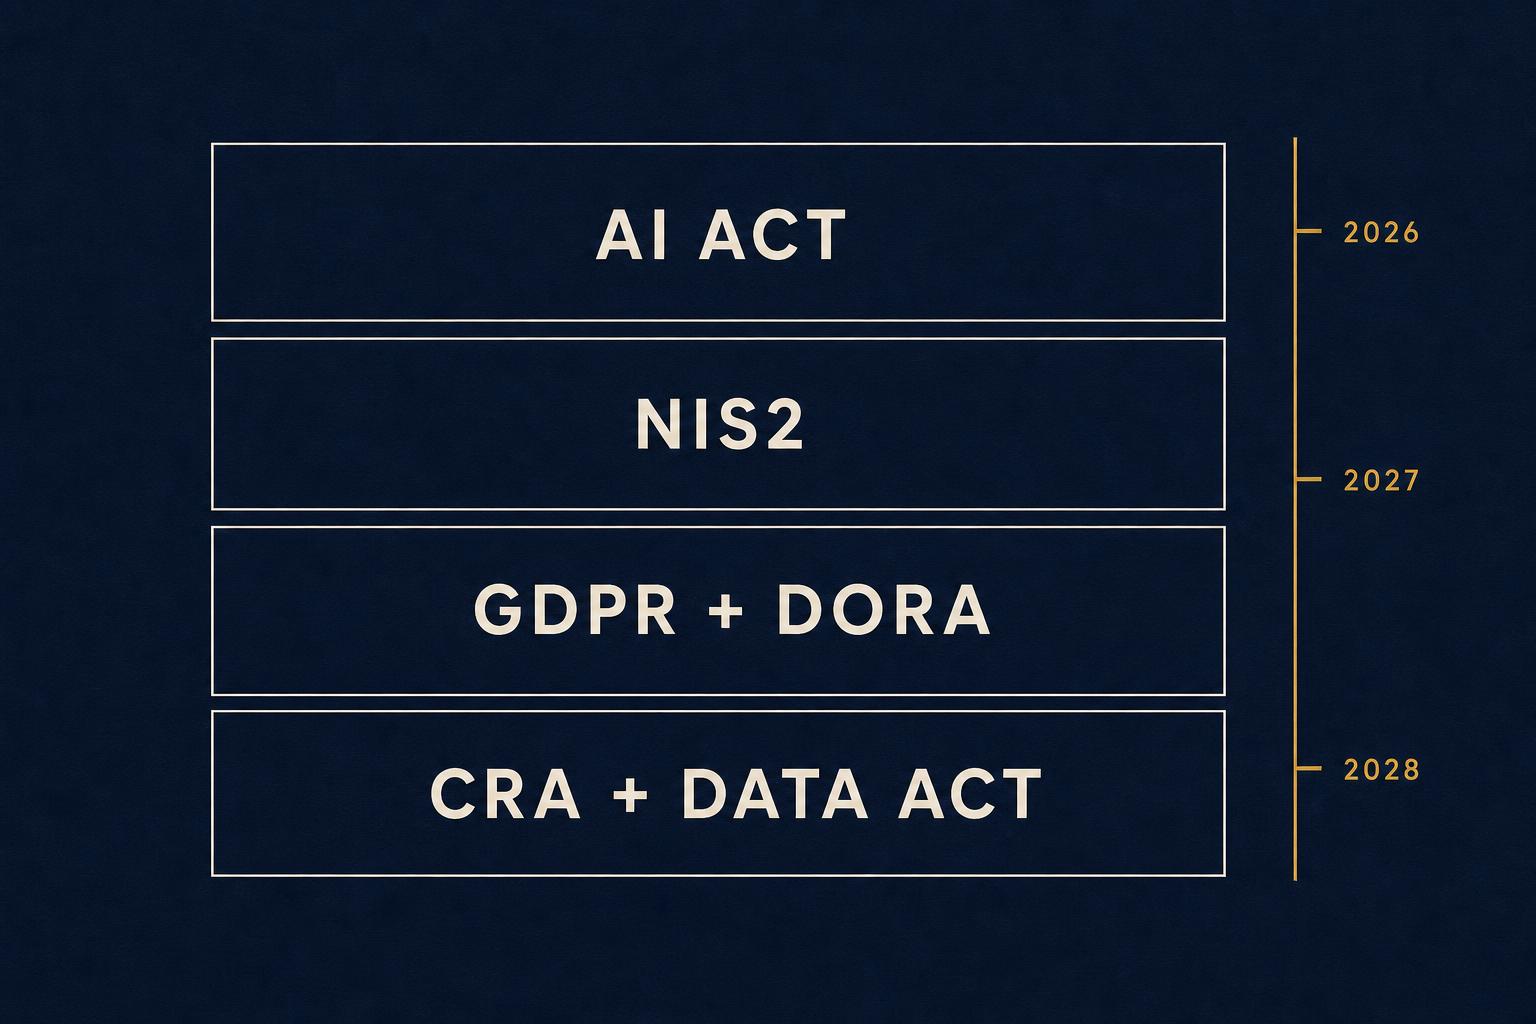
The flagship cluster: AI Act, NIS2, GDPR/DORA and the Cyber Resilience Act treated as one obligation map, with confirmed dates and primary sources.
NIS2 has 46 articles. Only a handful reach an AI vendor. A plain-language map of which ones bind you directly, which reach you through your customer, and what each demands.
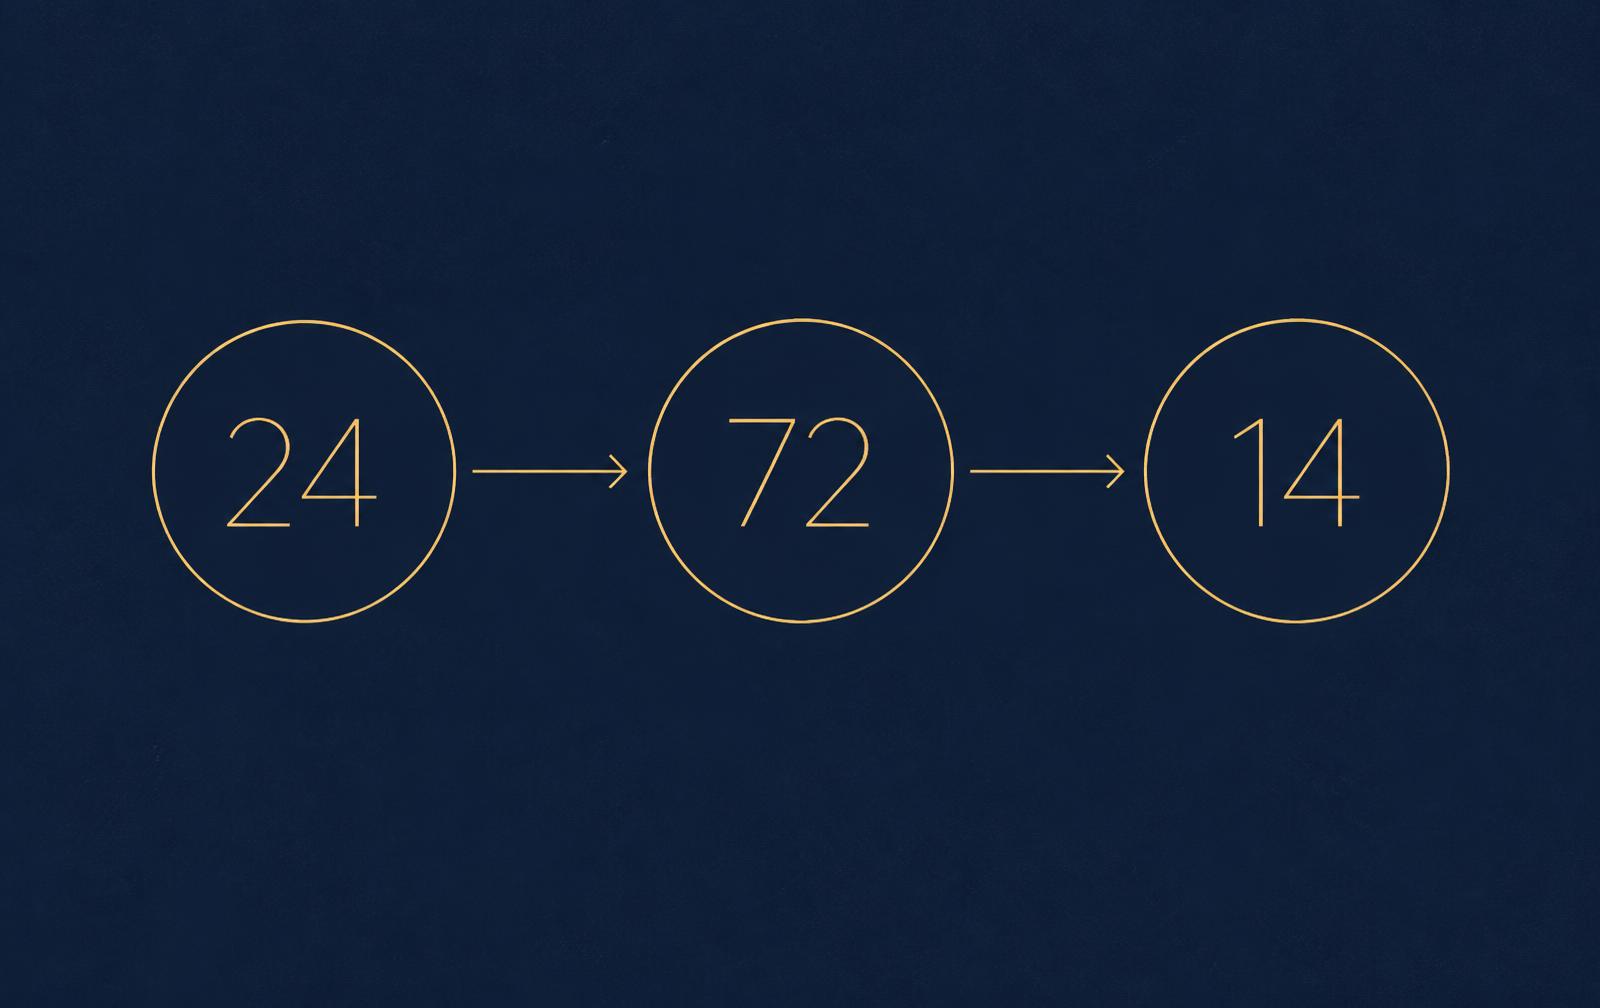
From 11 September 2026, Article 14 of the Cyber Resilience Act obliges manufacturers to report actively exploited vulnerabilities and severe incidents. The three deadlines, who files where, and what an AI vendor needs ready.
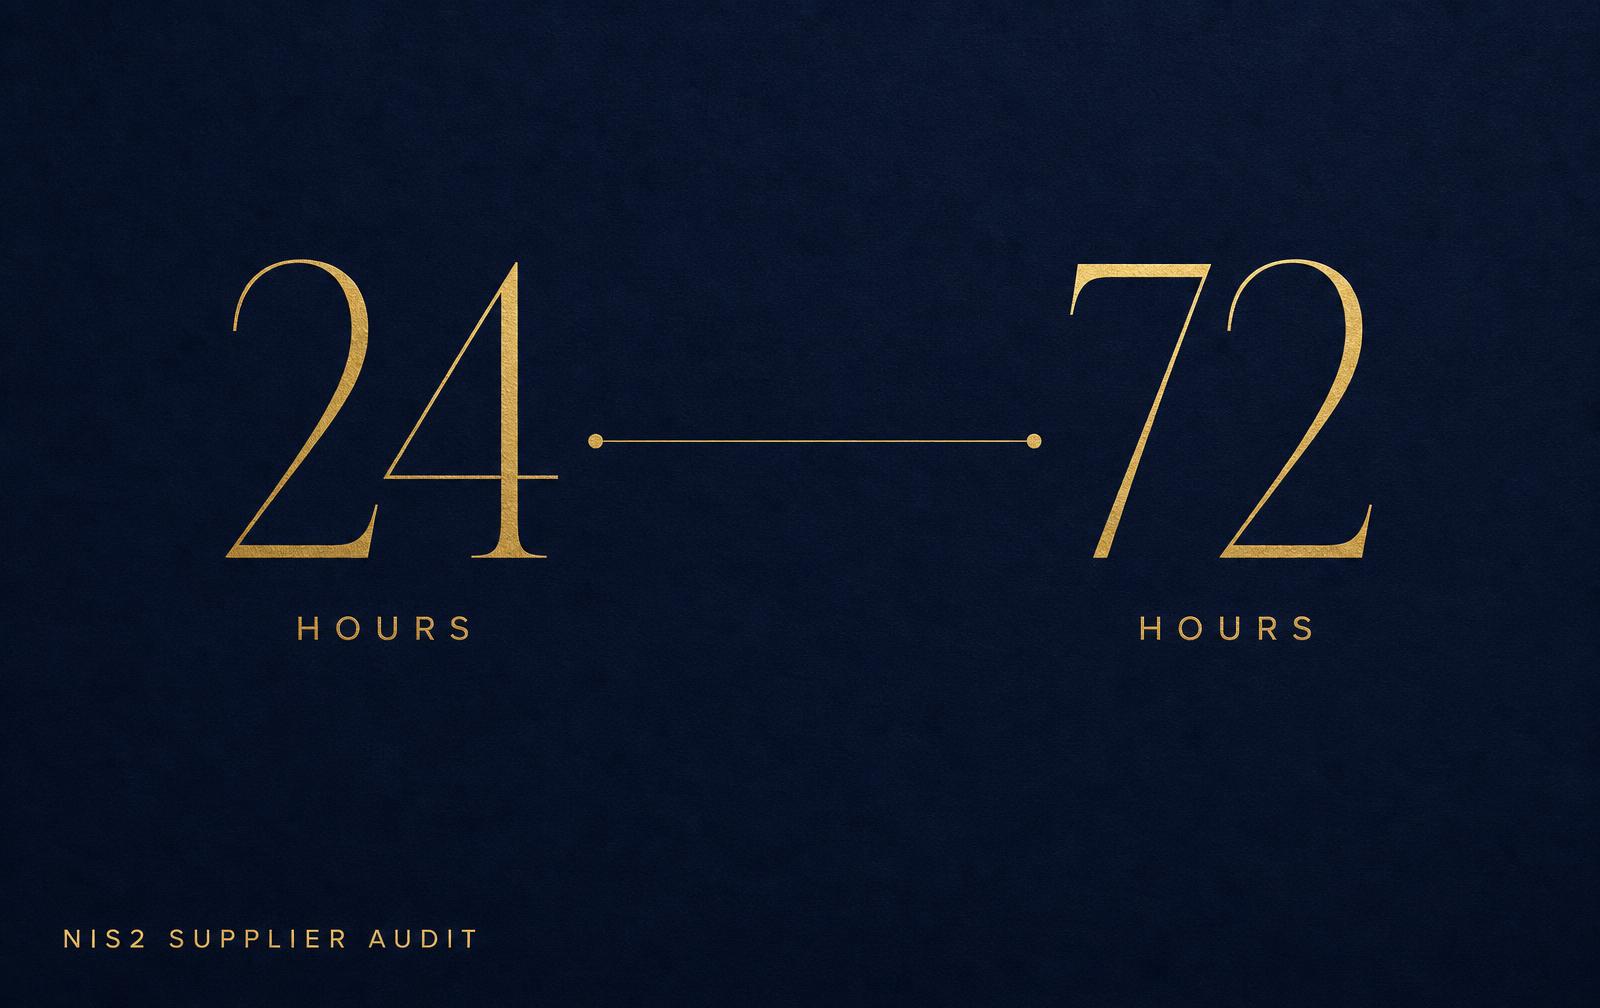
The 31 questions a NIS2 supply chain audit puts to an AI vendor, grouped by theme, each with the artefact that closes it and the answers that fail.
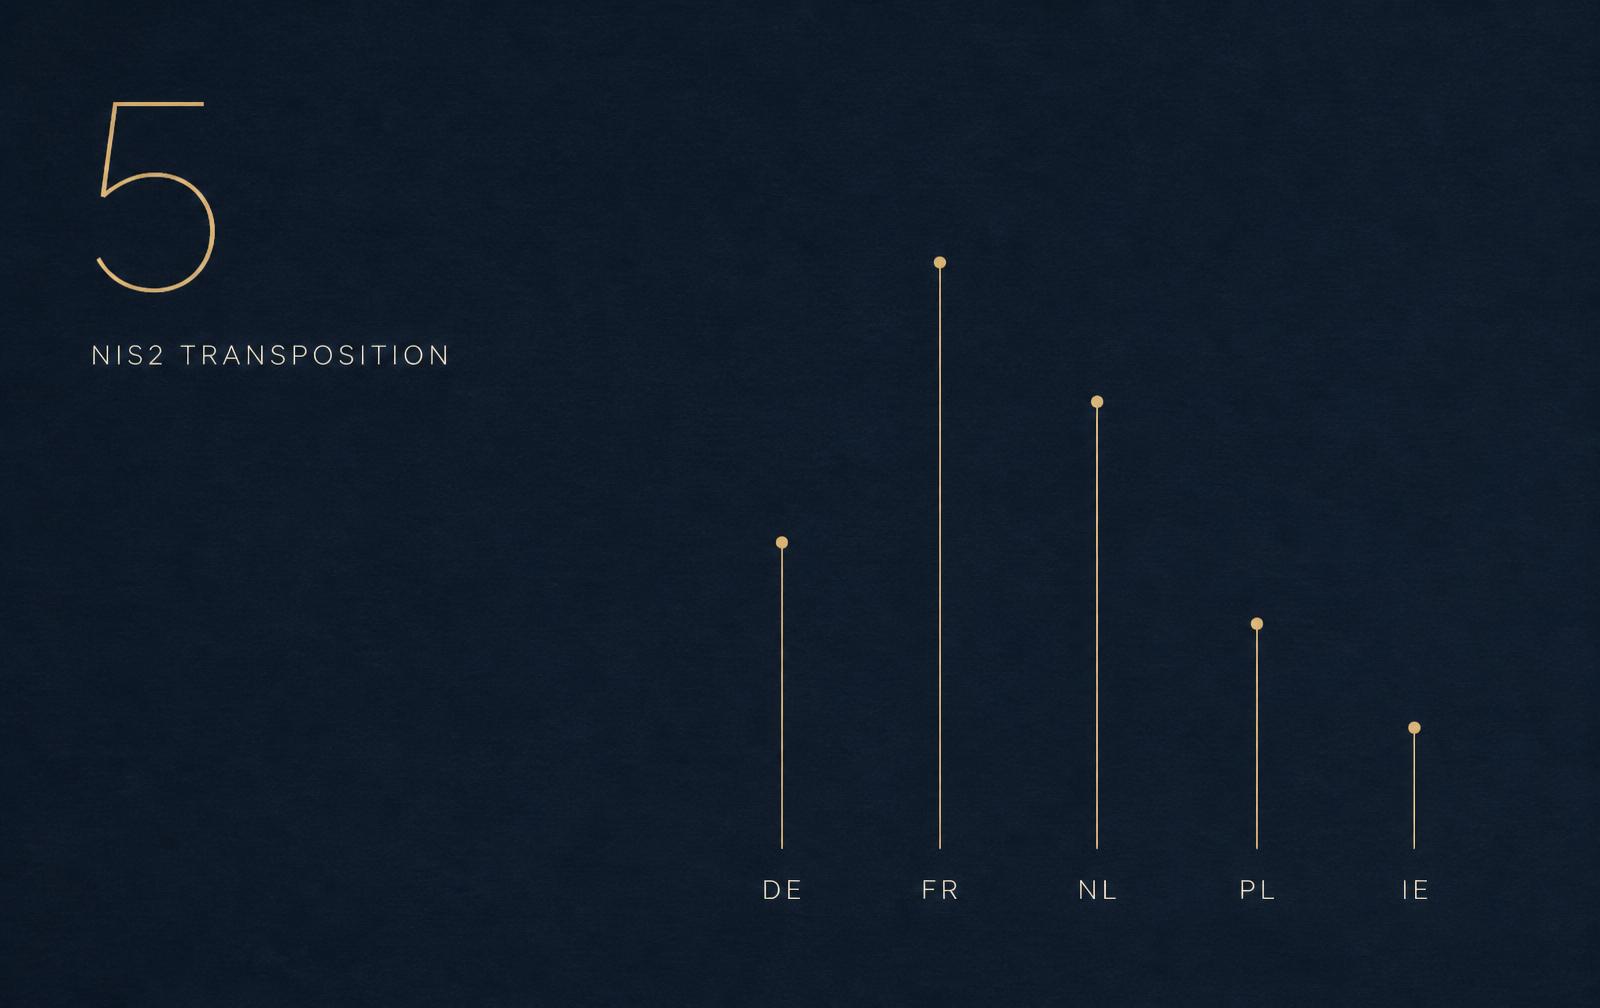
How uneven NIS2 transposition across Germany, France, the Netherlands, Poland and Ireland changes what an AI vendor must prove, and how to answer with one evidence pack.
NIS2 reaches AI vendors through the customer contract. The five evidence artefacts buyers request, the incident clocks, and what to prepare before the questionnaire.
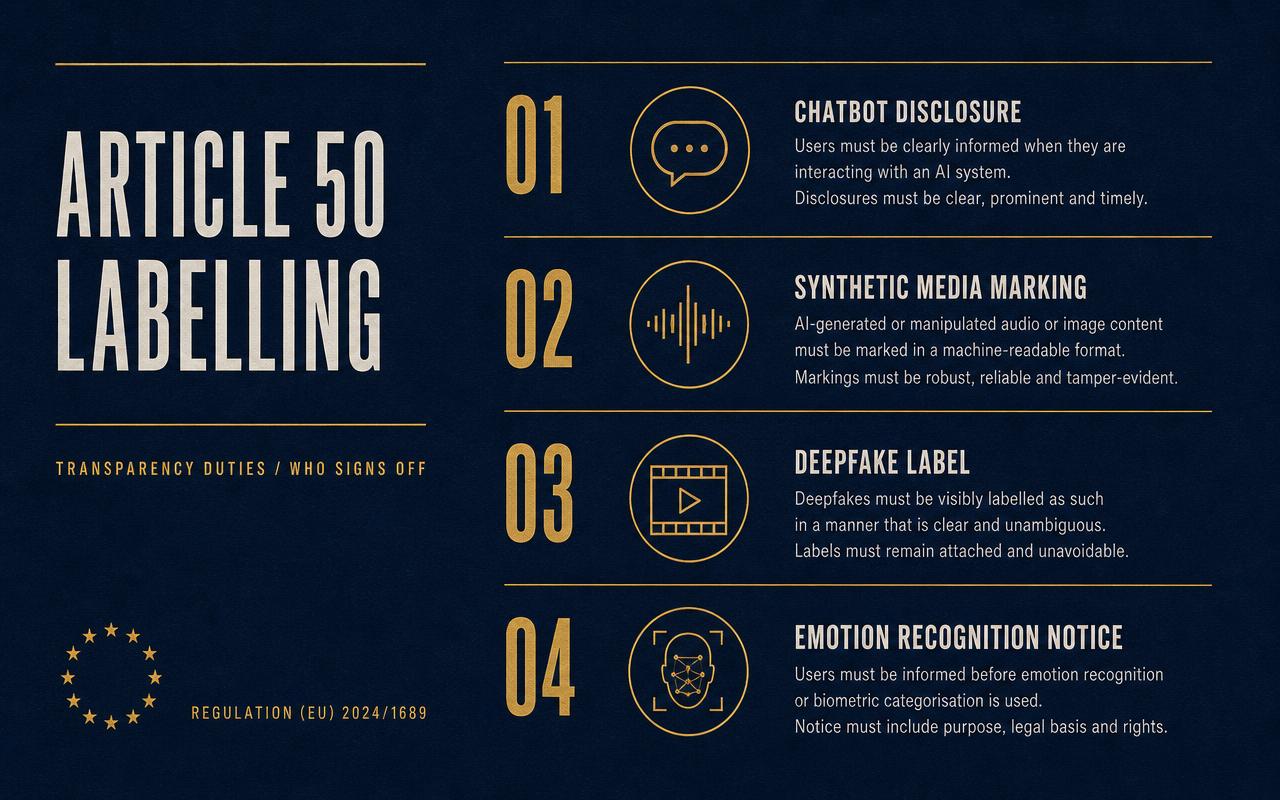
Article 50 has applied since 2 August 2026. Which outputs need a label, where the disclosure sits, and who owns the sign-off record.
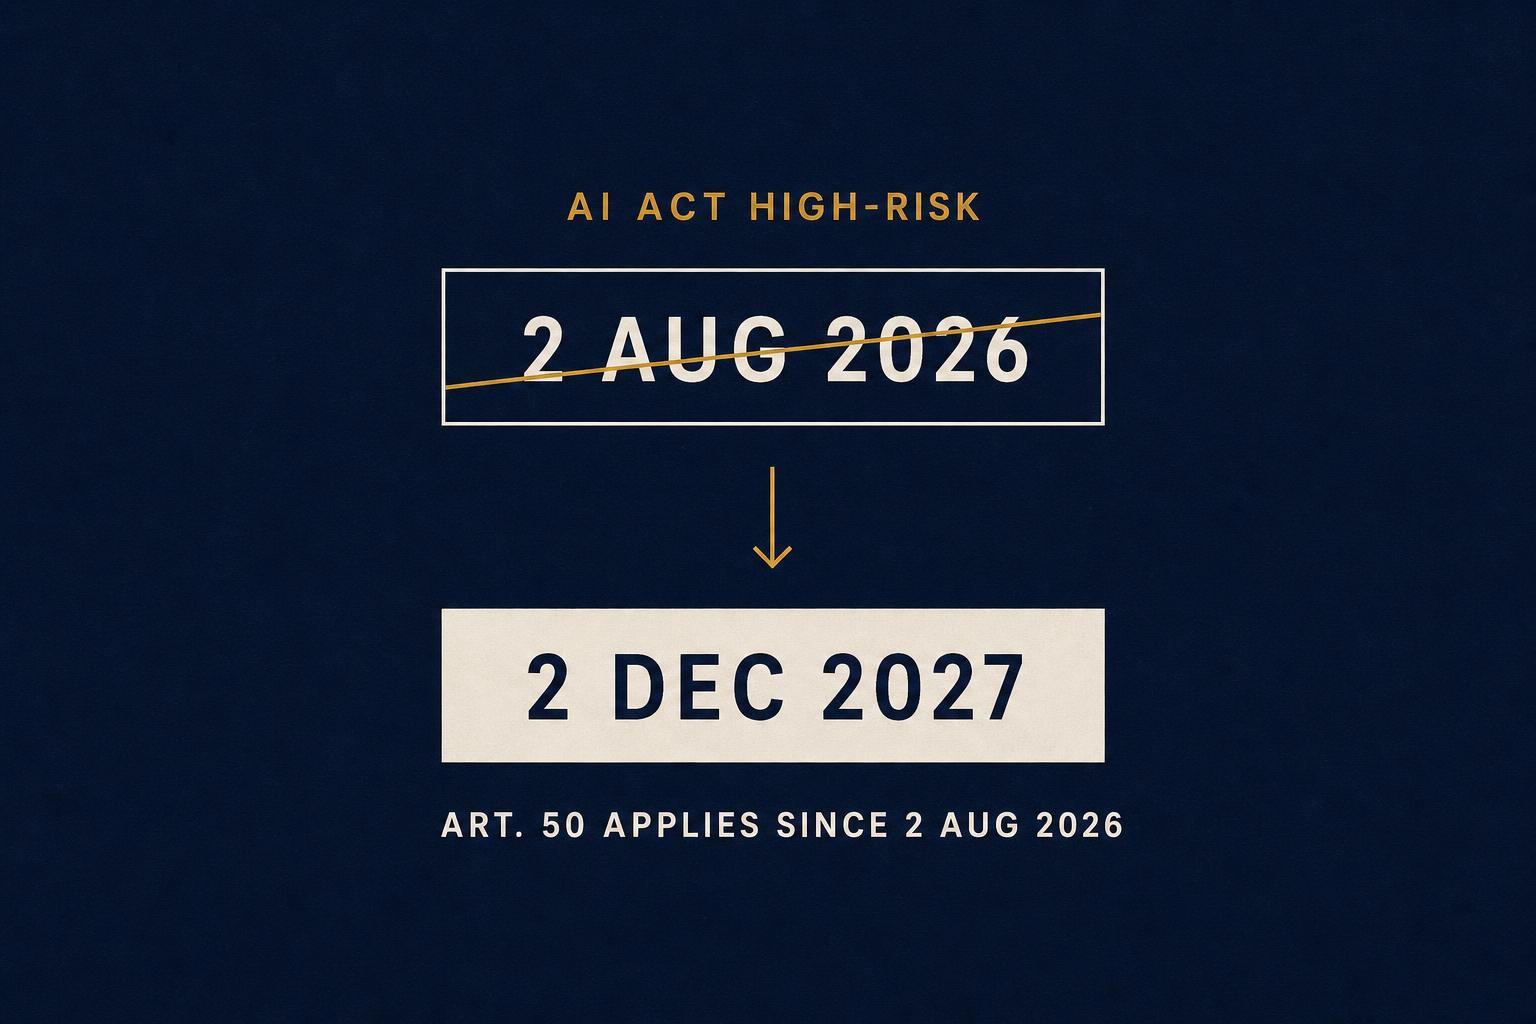
Only Article 50 applies from 2 August 2026; high-risk does not. What the Digital Omnibus changed in the AI Act calendar, with EUR-Lex sources.
One dated map of the AI Act, NIS2, GDPR/DORA and CRA obligations that hit AI vendors between August 2026 and August 2028, with EUR-Lex sources.
Next step
We build the artefacts your customers ask for, in the order they ask for them.
See the engagements